When setting up SAML with your identity service provider, you will need a SHA1 fingerprint. However, some identity service providers will give you an X.509 certificate that you need to convert.
Note: For more information on SAML, please see our What Is SAML Integration? article. For more information on obtaining your X.509 certificate from your specific identity service provider, please see the relevant article for your identity service provider in the SAML/SSO section of our Knowledge Base.
To convert your X.509 certificate into a SHA1 fingerprint, follow the steps below:
- Obtain the X.509 certificate from your identity service provider.
- Navigate to https://www.samltool.com/format_x509cert.php.
- Paste your X.509 certificate in the X.509 cert field.
- Click Format X.509 Certificate.
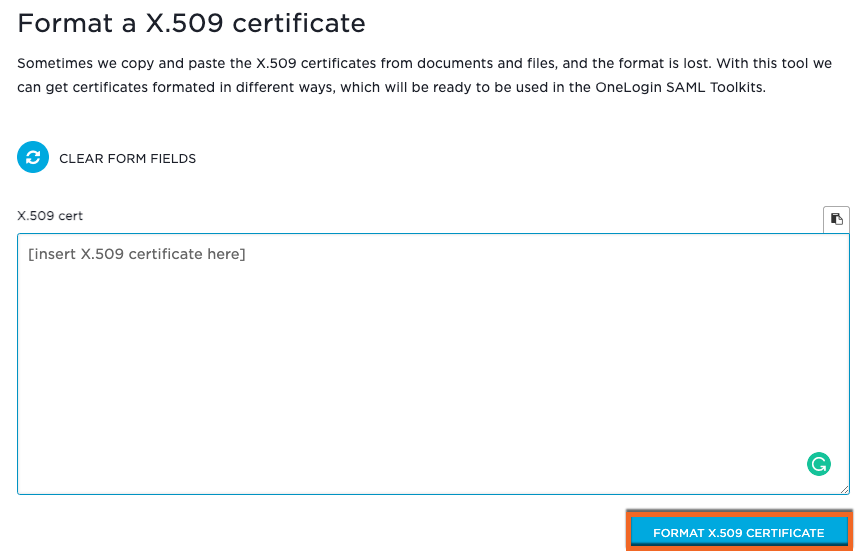
- Copy the certificate indicators in the X.509 cert with header field. Certificate indicators will display in between hyphens.
Note: If any line breaks display in the pasted certificate indicator, they will need to be deleted. Line breaks may cause the fingerprint to calculate incorrectly.
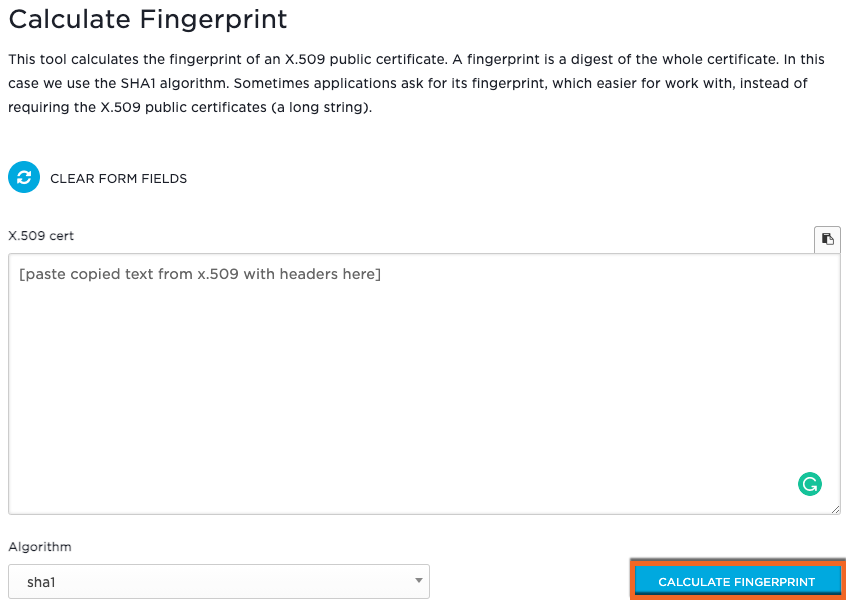
- Click Calculate Fingerprint from the toolbar on the left side of the screen.

- Paste the copied text into the X.509 cert field.
- Select sha1 from the Algorithm drop-down menu.
- Click Calculate Fingerprint.
Now that you have your SHA1 fingerprint, you can continue setting up your SAML login. For more information, visit our How to Set Up SAML Single Sign-on for the Security Awareness Training Platform article for more information.
Note: Make sure the email address that your users use to authenticate with SAML is either entered into the Email field or Email Aliases field of their user profile. However, only the email address listed in the Email field will receive training notification emails. For more information about adding information to user profiles, see our User Profile Guide.